Global Empire
Resources
Discover blogs, research, and success stories that help you innovate and deliver results faster.
Strategic BPO & Contact Center Research
Navigating business process outsourcing, contact center technology, and customer experience operations requires objective data, rigorous benchmarks, and transparent evaluation criteria. Global Empire Corporation’s research series analyzes the global BPO landscape across key industry verticals, regional labor markets, and operational capabilities to assist procurement leaders, COOs, and customer experience directors in making data-driven partner decisions.
Our market guides and competitive rankings assess enterprise and mid-market providers across four essential operational pillars:
- Delivery Model & Geographic Footprint: Evaluating onshore, nearshore, and offshore footprint distribution, labor arbitrage stability, language proficiencies, and business continuity architecture.
- Workforce Quality & Retention: Measuring frontline attrition rates, specialized agent training cycles, supervisor-to-agent coaching ratios, and quality assurance frameworks.
- Regulatory Compliance & Information Security: Validating adherence to rigorous compliance standards including HIPAA, PCI-DSS Level 1, SOC 2 Type II, TCPA, GDPR, and CASL regulations across customer touchpoints.
- Omnichannel Technology & AI Integration: Assessing cloud contact center infrastructure (CCaaS), conversational AI deflection, intelligent workforce management (WFM), and real-time speech analytics.
Explore our curated market rankings, operational guides, and industry analyses below to benchmark your program against top-tier industry standards.
Smarter insights. Better customer experiences.
 Top 15 BPO Companies in the USA & North America (2026)
 Top 15 BPO Companies for Airlines (2026)
 Top 15 BPO Companies for Logistics & Transportation (2026)
 Top 15 BPO Companies for Banking & Financial Services (2026)
 Top 15 BPO Companies for Insurance (2026)
 Real Estate BPO Companies: Top 15 Compared (2026)
 Top 15 Hotel BPO Companies (2026)
 Top 15 Call Center Companies in Australia (2026)
 Top 15 Call Center Companies in Ireland (2026)
- Top 15 Call Center Companies in Toronto (2026)
 Telemarketing Companies in the Philippines: Buyer Guide
- Insurance Verification: Administrative Support Scope
- What Is Data Labeling? A Buyer Guide
- Advantages of Outsourcing: How to Test the Business Case
- Health and Wellness Customer Support: Scope Guide
- Intelligent Automation: Human Review and Handoffs
- Colombia Customer Support: A Delivery Planning Guide
- Customer Satisfaction Score: CSAT Measurement Guide
- Finance and Accounting BPO: Scope and Controls
- IT Project Outsourcing: Ownership and Handoffs
- Learning and Development for Customer Support Teams
- Software Outsourcing for Startups: Scope Checklist
- Video Editing Outsourcing: Brief and Review Workflow
- Payment Integrity: Administrative Review Boundaries
- Payroll Processing: Handoff and Verification Controls
- Airlines and Aviation Customer Support: Scope Guide
- Care Coordination Support: Administrative Boundaries
- Churn Rate: Measurement and Customer Support Review
- Cloud Infrastructure: Support Handoffs and Ownership
- Digital Operations: Exceptions and Human Review
- Digital Payments Support: Routing and Escalation
- Dominican Republic Call Centers: Buyer Planning Guide
- Electronic Medical Records: Support Access Boundaries
- Loan Processing Support: Administrative Boundaries
- Managed Service Pricing: Compare Written Scope
- Insurance Verification Outsourcing: Scope Checklist
- Mobile App Customer Support Outsourcing
- Call Center Case Studies: An Evidence Review Framework
- Telephone Survey Call Centers: Scope and Quality
- Mexico Nearshore Call Centers: Buyer Planning Guide
- Reservation Call Centers: Booking and Change Support
- Disaster Response Call Centers: Administrative Intake
- Product Recall Call Centers: Intake and Escalation
 Customer Experience Analytics: How to Turn CX Data Into Decisions
 Call Center Outsourcing Cost in 2026: A Practical Pricing Guide
 BPO vs. Call Center: Key Differences and Which One You Need
 In-House vs. Outsourced Customer Service: Costs, Pros, and Cons
 How to Choose a BPO Partner: A Practical Buyer’s Checklist
 Outsourced Lead Generation: How It Works and When It Pays Off
 Technical Support Outsourcing: A Complete Guide for 2026
 Outsourcing Live Chat Support: A Practical Guide
 Email Support Outsourcing: How to Scale Without Losing Quality
 Back Office Outsourcing: What to Transfer and What to Keep
 Outsourced Sales Development: Building Pipeline Without Building a Team
 Inbound vs. Outbound Call Center Outsourcing: Which One Do You Need?
- US-Based Call Center Outsourcing: Onshore, Nearshore and Offshore Compared
 B2C Telemarketing: How Consumer Outbound Programs Actually Work
 Telemarketing Outsourcing: A Buyer's Guide
 How to Evaluate Customer Service Outsourcing Companies
 Financial Services Call Center Outsourcing: A Compliance-First Guide
 Ecommerce Customer Service Outsourcing: Peaks, Channels and Returns
 Outsourcing Customer Service for Small Business: What Actually Works
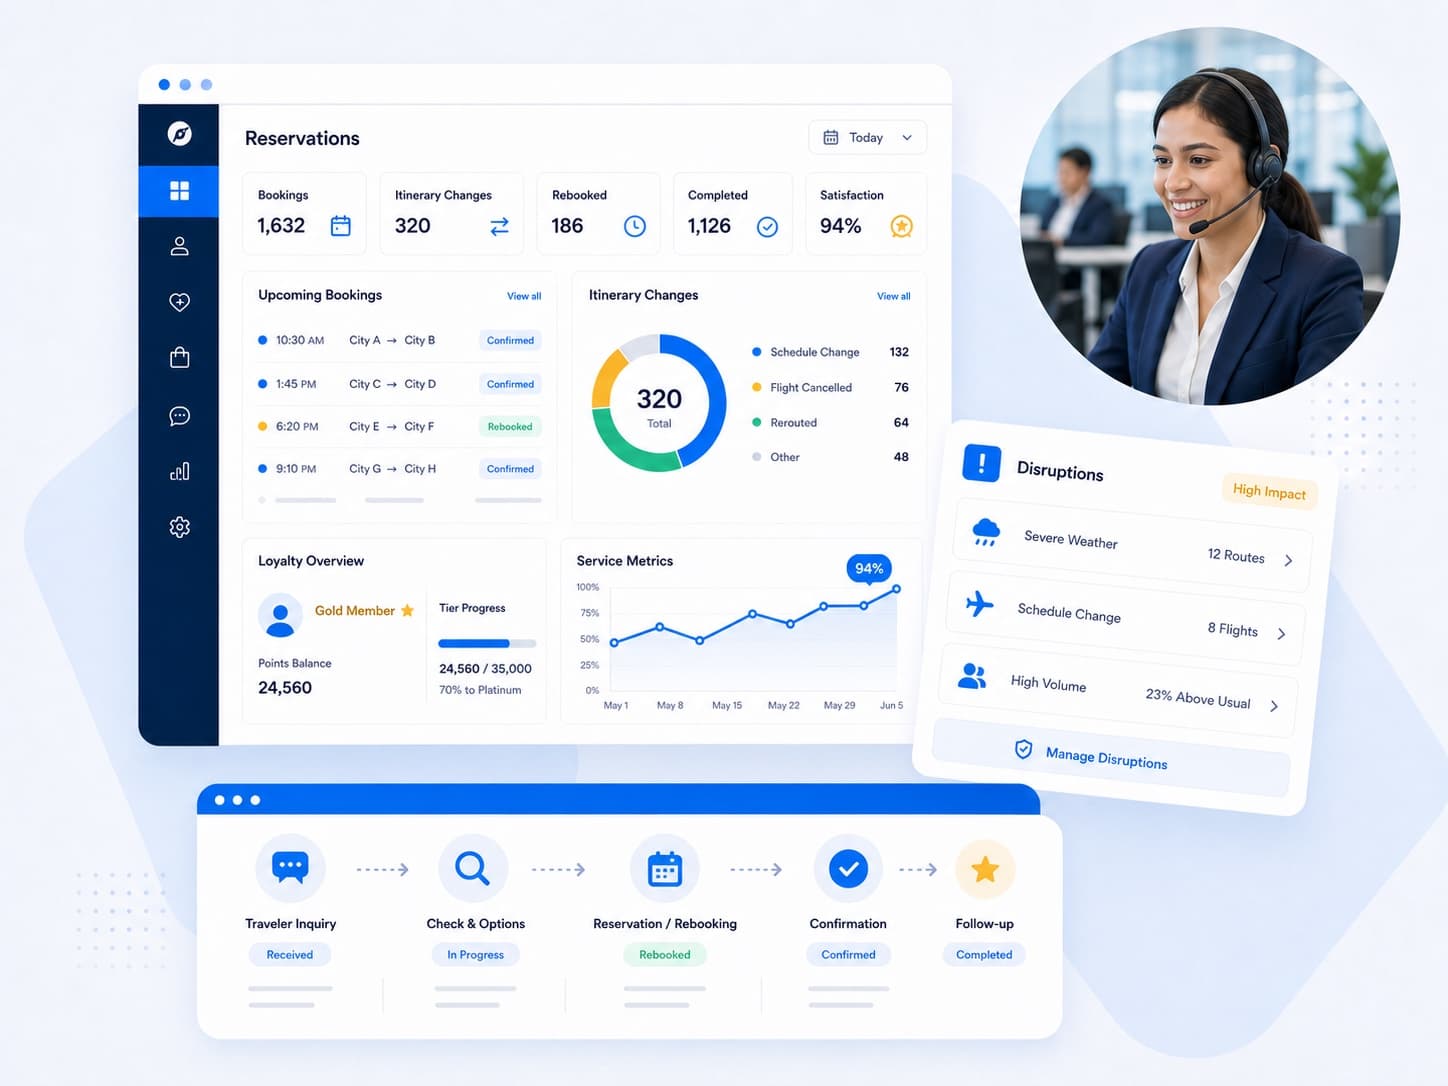 Hospitality Call Center Outsourcing: Reservations, Guests and Peak Demand
 AI vs Human Call Centers: Where Automation Helps and Where It Loses Customers
 Will AI Replace Call Center Agents? What Actually Changes
- How to Outsource Customer Service: The Process, Step by Step
 Call Center RFP Guide: What to Include and How to Score Vendors
 Benefits of Outsourcing Call Center Services (and When It's the Wrong Move)
 Onshore vs Nearshore vs Offshore Call Centers: How to Choose
 Legal Call Center Outsourcing: Intake, Confidentiality and After-Hours Coverage
 Manufacturing Call Center Outsourcing: Order Desk, Dealer Support and Warranty Lines
 Retail Call Center Outsourcing: Peak Season, WISMO and Returns Done Right
 Healthcare Customer Support Outsourcing: Patient Access Without the Compliance Risk
 Telecom Call Center Outsourcing: Churn, Tier-1 Tech Support and Billing at Volume
 Inbound Lead Generation Services: Turning Demand You Already Have into Pipeline
 How a Call Center Grows Your Business: The Five Revenue Mechanics
- Answering Service vs Call Center: Which One Do You Need?
 What Drives Answering Service Cost (And What to Ask Before You Buy)
 After-Hours Answering: Designing Coverage That Pays for Itself
- HIPAA and Your Answering Service: What Actually Has to Be True
- First Call Resolution: The Metric Most Contact Centers Measure Wrong
 CSAT, NPS, CES and the Metrics Worth Putting on a Dashboard
- How to Reduce Call Abandonment Without Just Adding Agents
- Call Center Attrition: What It Really Costs and What Reduces It
 Seasonal Support Staffing: Covering a Peak Without Carrying It All Year
- PCI Compliance in a Call Center: Where Card Data Actually Leaks
 Multilingual Customer Support: Staffing It Properly, Not Translating It
- Writing a Call Center SLA That Means Something
- What Is BPO? Business Process Outsourcing, Explained Properly
- What Is a Call Center? How They Work, and When You Need One
- Call Center Outsourcing Implementation Plan: A 90-Day Launch Guide
- Call Center Data Security Checklist for Outsourcing Buyers
- Omnichannel Customer Service: How to Connect Phone, Chat and Email
- Call Center Quality Assurance: A Practical Scorecard
- How to Compare Call Center Outsourcing Quotes
- Call Center Pricing Models Explained: Per-Minute, Per-Hour, Per-Call and Per-Resolution
- How Outbound Call Center Pricing Works: Per-Hour, Per-Lead, Per-Appointment and Per-Sale
- What Drives Technical Support Outsourcing Cost
- The Hidden Costs of Call Center Outsourcing (and How to Surface Them)
- Call Center Outsourcing Cost Per Hour: What an Hourly Rate Actually Buys
- Answering Service Pricing Models: Per-Minute, Per-Call, Per-Message and Flat Monthly
- How Inbound Call Center Pricing Works: Service Level, Intervals and the Seat
- The Cost of 24/7 Customer Support: Why Round-the-Clock Is Not Three Times Business Hours
- Insurance Call Center Outsourcing: What Carriers and Agencies Should Look For
- SaaS Customer Support Outsourcing: Scaling Support Without Slowing the Product
- Logistics Call Center Outsourcing: Support That Keeps Freight Moving
 Energy and Utilities Call Center Outsourcing: Billing, Outages and the Regulated Line
 Automotive Customer Service Outsourcing: Dealers, OEMs and the Connected Car
 Travel Customer Service Outsourcing: Booking, Disruption and the 3am Call
 Education Call Center Outsourcing: Enrollment, Student Support and the Seasonal Peak
- When to Outsource Customer Service: The Signals That Say It Is Time
- Average Handle Time (AHT): What It Measures and How to Improve It Honestly
- Call Center Occupancy: The Metric That Looks Like Efficiency and Becomes Burnout
- Call Center Forecasting: Getting the Volume Right Before You Staff to It
- Call Center Workforce Management: Forecast, Schedule, Adhere, Repeat
 Schedule Adherence: The Metric That Decides Whether the Plan Survives the Day
 NPS vs CSAT vs CES: Which Customer Experience Metric Actually Tells You Something
- The Risks of Call Center Outsourcing, and How to Manage Each One
 Vendor Management for Outsourced Contact Centers: Owning the Relationship
- What Is Appointment Setting, and When Does Outsourcing It Pay Off?
- B2B Appointment Setting: Filling a Complex Pipeline Without Burning the Brand
- Lead Qualification Outsourcing: Sending Sales Only the Leads Worth Their Time
 Cold Calling Outsourcing: Making It Work Without Wasting Money or Goodwill
 Customer Retention Outsourcing: Keeping Customers Is Cheaper Than Winning Them
- Call Center Agent Training: Why Onboarding Decides Whether Outsourcing Works
 Help Desk vs Call Center: Which One Does Your Business Actually Need?
- Inbound Sales Outsourcing: Converting the Calls That Are Already Interested
 Social Media Customer Service Outsourcing: Support Where Everyone Is Watching
 Text Message Customer Service: Outsourcing the Channel Customers Actually Answer
- Customer Onboarding Outsourcing: The First 90 Days Decide Whether They Stay
 Order Management Outsourcing: The Back Office Behind Every Sale
 Returns Management Outsourcing: Turning a Return Into a Retained Customer
 Complaint Management Outsourcing: The Complaint Is a Gift, If You Handle It Right
 Self-Service vs Live Agent Support: Getting the Balance Right
- Business Continuity for Contact Centers: Answering When Something Goes Wrong
- Voice of the Customer: Turning What Customers Say Into What You Fix
- Customer Journey Mapping: Seeing the Experience the Way the Customer Does
 Call Recording Compliance: The Rules Behind Recording Customer Calls
- IVR Best Practices: Automation That Helps Callers Instead of Trapping Them
- Call Routing and Skills-Based Routing: Getting the Caller to the Right Agent
 Customer Service Scripts: When They Help, When They Hurt, and How to Write Them Right
- First Response Time: The Metric Customers Feel Before Any Other
- Customer Satisfaction Surveys: Asking in a Way That Actually Tells You Something
- Government Call Center Outsourcing: Citizen Service Under Public Scrutiny
- Nonprofit Call Center Outsourcing: Donor Care That Protects the Relationship
- Gaming Customer Support Outsourcing: Players, Communities and the 3am Bug
- Construction Call Center Outsourcing: Answering for a Business Run From the Field
- Real Estate Call Center Outsourcing: Never Missing the Lead That Closes
- Restaurant Customer Service Outsourcing: Orders, Reservations and the Rush
- Subscription Customer Service Outsourcing: Where Churn Is Fought on the Phone
- Fintech Customer Support Outsourcing: Trust, Speed and the Regulated Money Question
- Mortgage Customer Service Outsourcing: Servicing the Loan Under Heavy Regulation
- Cruise Line Customer Service Outsourcing: Booking, Voyage and the Disruption at Sea
- Car Rental Customer Service Outsourcing: Reservations, Roadside and the Dispute
- Medical Device Support Outsourcing: Technical Help That Is Also a Safety System
- Food Delivery Customer Service Outsourcing: Three Sides, One Order, No Time
- Rideshare and Gig Driver Support Outsourcing: Keeping the Supply Side on the Road
- Debt Collection Outsourcing: Recovering More by Collecting the Right Way
- Pharmaceutical Patient Support Outsourcing: Access, Adherence and the Adverse Event
- Overflow Call Handling: Catching the Calls Your Team Cannot
- De-Escalation in Customer Service: Turning an Angry Call Around
- Proactive Customer Service: Reaching Out Before the Customer Has To
- Escalation Management: Getting the Hard Cases to the Right Place Fast
- Weekend and Holiday Call Coverage: Being Reachable When Competitors Are Not
- Warm Transfer vs Cold Transfer: The Small Difference Customers Feel Most
- Over-the-Phone Interpretation: Serving Customers in Any Language
- Abandoned Cart Recovery Outsourcing: Winning Back the Sale That Almost Happened
- Scaling Customer Support: Growing the Team Without Breaking the Experience
- Handling High Call Volume: Staying in Control When the Phones Light Up
- Reducing Hold Times: The Wait Customers Hate and How to Cut It
- Building a Customer Service Knowledge Base That Agents Actually Use
 Customer Support for Startups: Punching Above Your Weight Early
- Customer Service Team Structure: Designing the Team Around the Work
- Call Center and BPO Glossary: Contact Center Terms Defined
- The North America BPO Market: Onshore to Nearshore
- Cold Calling Scripts: Openers, Objections and a Call Structure
- Real Estate Cold Calling: Scripts, Lists and Rules
- What Is an SDR? The Sales Development Rep Role Explained
- What Is Telecom BPO? Telco BPO Services Explained
- What Is BFSI BPO? Banking & Financial Services BPO
- What Is Retail BPO? Services, Examples and Uses
- What Is Healthcare BPO? Services, HIPAA and Uses
- What Is Education BPO? Services for Schools & Colleges
- TCPA Compliance for Call Centers: A Practical Guide
- Call Center vs Contact Center: What's the Difference?
- What Is Nearshore Outsourcing? Meaning, Pros and Cons
- What Is Customer Service Outsourcing? A Plain Guide
- What Is a Virtual Receptionist? How the Service Works
- What Is an Answering Service? Types and How It Works
- What Is IVR? Interactive Voice Response Explained
- HIPAA Compliance for Call Centers: What the Rules Require
- Risks of Offshore Call Centers and How to Manage Them
- GDPR for Call Centers: Handling EU Customer Data
- PIPEDA for Call Centers: Canadian Privacy Rules Explained
- What Is Back Office Outsourcing? Functions and Examples
- BPO for Regulated Industries: What Providers Must Prove
- Call Center vs BPO: What Is the Difference?
- SOC 2 for Call Centers: What the Report Means
- What Is Offshore Outsourcing? Definition, Models and Fit
- BPO vs KPO: What Is Knowledge Process Outsourcing?
- Tier 1, Tier 2 and Tier 3 Support: What Each Level Handles
- What Is Lead Generation Outsourcing? How It Works
- Call Center Quality Assurance: Scorecards and Coaching
- What Is First Call Resolution? Definition and Measurement
- Average Handle Time Explained: Formula and Components
- What Is Omnichannel Customer Support? How It Works
 What Is Technical Support Outsourcing? Tiers and SLAs
- What Is Live Chat Outsourcing? Staffing and Quality
- What Is Healthcare Payer BPO? Health Plan Services
- Top 15 International BPO Companies in the World (2026)
Sources and References
The laws, standards and certifications this page refers to, linked to their official text or publisher.
- HIPAA (Health Insurance Portability and Accountability Act), U.S. Department of Health & Human Services: privacy and security rules for protected health information.
- PCI DSS (Payment Card Industry Data Security Standard), PCI Security Standards Council: handling of payment card data.
- SOC 2, AICPA & CIMA: independent audit of a service organization's security controls.
- ISO/IEC 27001, International Organization for Standardization: information security management systems.
- TCPA (Telephone Consumer Protection Act), 47 U.S.C. § 227, Legal Information Institute, Cornell Law School: consent rules for autodialed, prerecorded and text outreach.
- Telemarketing Sales Rule, 16 CFR Part 310, Electronic Code of Federal Regulations: disclosures, calling hours and abandoned-call limits for telemarketing.
- National Do Not Call Registry, Federal Trade Commission: numbers that telemarketers may not call.
- FERPA (Family Educational Rights and Privacy Act), U.S. Department of Education: privacy of student education records.
- STIR/SHAKEN caller ID authentication, Federal Communications Commission: caller ID authentication on voice networks.
- PIPEDA (Personal Information Protection and Electronic Documents Act), Office of the Privacy Commissioner of Canada: private-sector privacy law in Canada.
- Canada's Anti-Spam Legislation (CASL), S.C. 2010, c. 23, Justice Laws Website, Government of Canada: consent rules for commercial electronic messages in Canada.
- Québec Law 25 (privacy), Commission d'accès à l'information du Québec: privacy obligations for organizations operating in Québec.
- UK GDPR, Information Commissioner's Office: data protection law in the United Kingdom.
- GDPR, Regulation (EU) 2016/679, EUR-Lex, Publications Office of the European Union: data protection law in the European Union.